The Swiss Potato With a Chinese Accent
The Potato Files: Part I
Let's start with a pretty simple question: Is TatoTalk a honeypot?
And it turns out to be much harder to answer than expected. The more you look at TatoTalk, the less obvious it becomes who you're actually trusting in the first place.
And before we get to the encryption, let's start with the boring part:
Tato may be the new name, but the trail starts with Potato and it gets weird almost immediately.
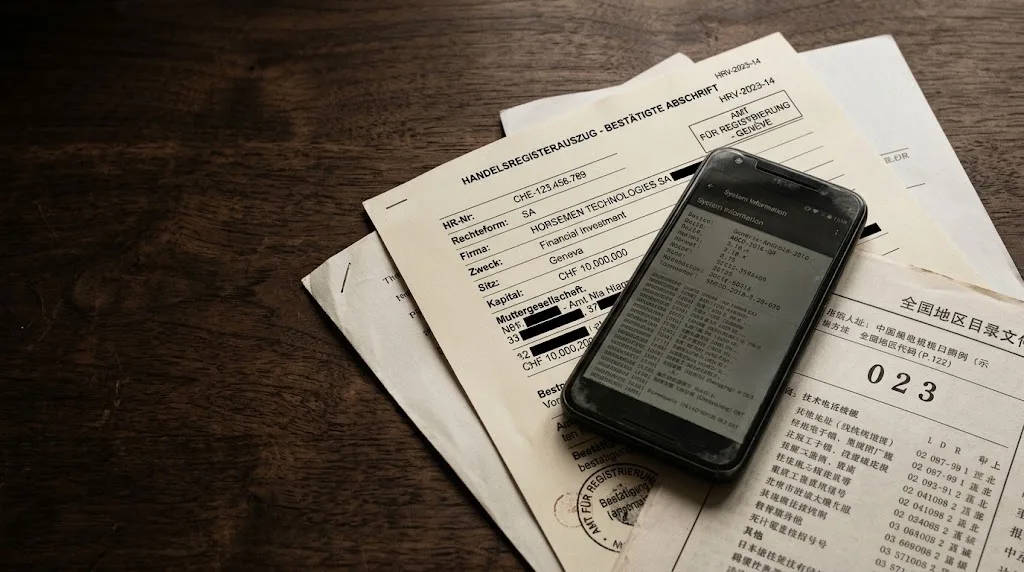
PART I / WHO MADE THE POTATO?Switzerland, apparently.
For years, Potato was published under Horsemen Technologies SA, a Swiss corpo registered in Sarnen. Which sounds normal enough until you look at what Horsemen actually was.
Its registered purpose was to manage trademarks, patents, licences and other IP rights. Software development wasn't even mentioned.
But that alone just means that "published by a Swiss company" and "made by Swiss devs" are two very different things.
You might want to say something like "no shit Sherlock!", but keep reading.
The Swiss potato starts looking Chinese
So, Potato always had that strong Chinese footprint (pages, miniapps, CN ecosystem features, etc.)
For a long time that could easily be written off as simple market fit. I mean, China is a massive market, and users like WeChat-style features, no mystery there.
Then we looked at the original Android signing certificate.
C=023
ST=cq
L=zhcq
O=potato
OU=potato
CN=team
The certificate became valid on 21 December 2016.
Horsemen Technologies SA was incorporated in Switzerland two days later.
Now, Android certificate fields are self-declared. You can type whatever bullshit you want into them.
But 023 happens to be Chongqing’s telephone area code.
And cq is, unsurprisingly, Chongqing.
zhcq is less obvious, and I’m not going to pretend we know exactly what whoever created the key meant by it.
Still, that's a pretty fucking Chongqing-looking certificate for a supposedly Swiss messenger.
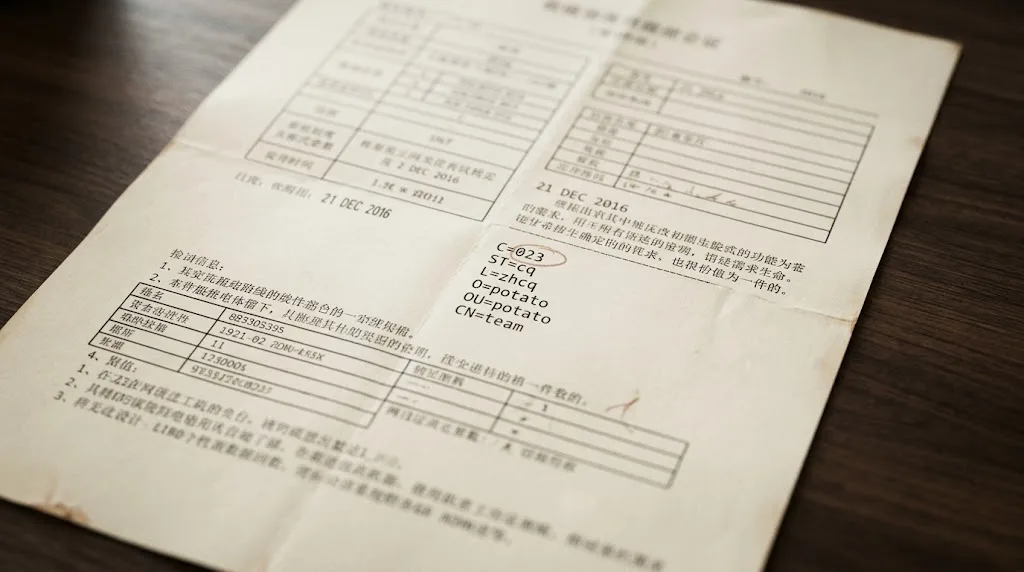
ANDROID SIGNING CERTIFICATE / 21 DEC 2016At that point, "Swiss app with a big Chinese userbase" starts feeling a little too convenient.
Especially because the Chongqing trail comes back later.
And when it does, it comes back attached to a cybersecurity company with a very interesting résumé and we will save that shitshow for Part II.
For now, there is another problem.
Tato can't seem to decide how its encryption works
The current App Store page makes a pretty bold promise:
Every message, call, and file transfer is protected by end-to-end encryption.
Then you open Tato’s own privacy policy and it starts talking about Cloud Chats: messages, photos, videos and documents stored on Tato’s servers so they can sync across your devices.
A few paragraphs later, Secret Chats suddenly appear, and those are described as end-to-end encrypted.
So... which one is it?
Because "every message is E2EE" and "Cloud Chats + separate E2EE Secret Chats" are not the same security model.
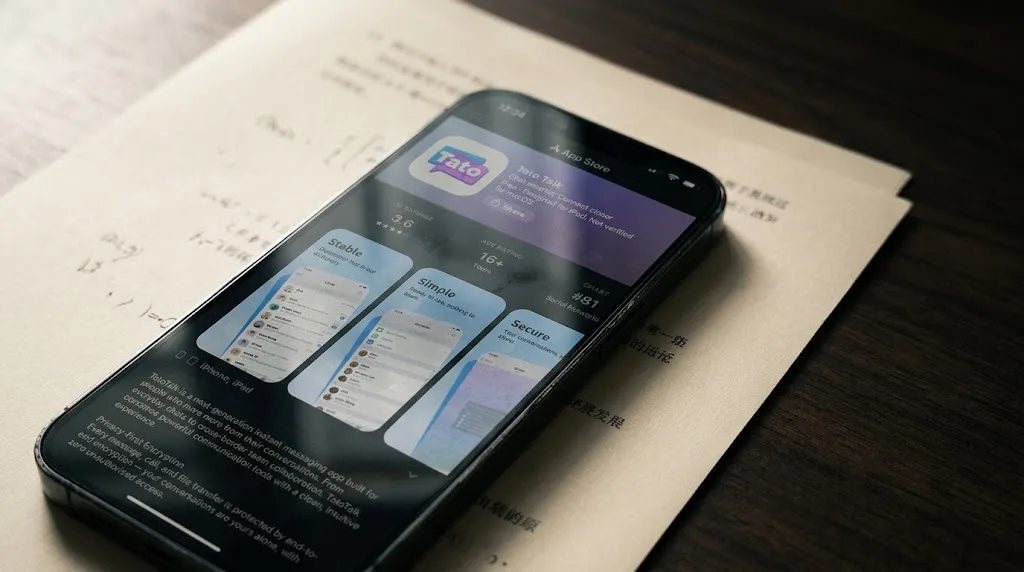
APP STORE / PRIVACY POLICYAnd then the privacy policy gets even funnier, because...
It reads suspiciously like Telegram’s old one.
Not in the generic "both messengers mention encryption" way though.
I mean the same Cloud Chats / Secret Chats split, the same synced contacts stuff, the same account-deletion logic, even the same oddly specific joke about not sending users marketing or "we miss you" bullshit.
Somebody apparently liked Telegram’s legal department enough to preserve the jokes too.
So either Tato actually moved everything to universal E2EE and nobody bothered updating the privacy policy, or the App Store page is straight up lying.
In my opinion, for a privacy messenger, that is a pretty retarded place to leave ambiguity.
And then the Swiss company disappears
This part is almost too convenient.
Horsemen Technologies SA was dissolved by shareholder resolution in December 2025.
A few months later, TatoTalk appears under a Malaysian publisher.
BACK END TECH SDN. BHD.
What I couldn’t find was the boring part: any public explanation of how the transition actually happened.
No acquisition note. No ownership announcement. No explanation of what happened to the backend, user accounts, infrastructure, or whatever else actually changed hands.
Maybe that explanation exists somewhere buried in corporate paperwork.
But from the outside it looks a lot like Potato simply changed passports.
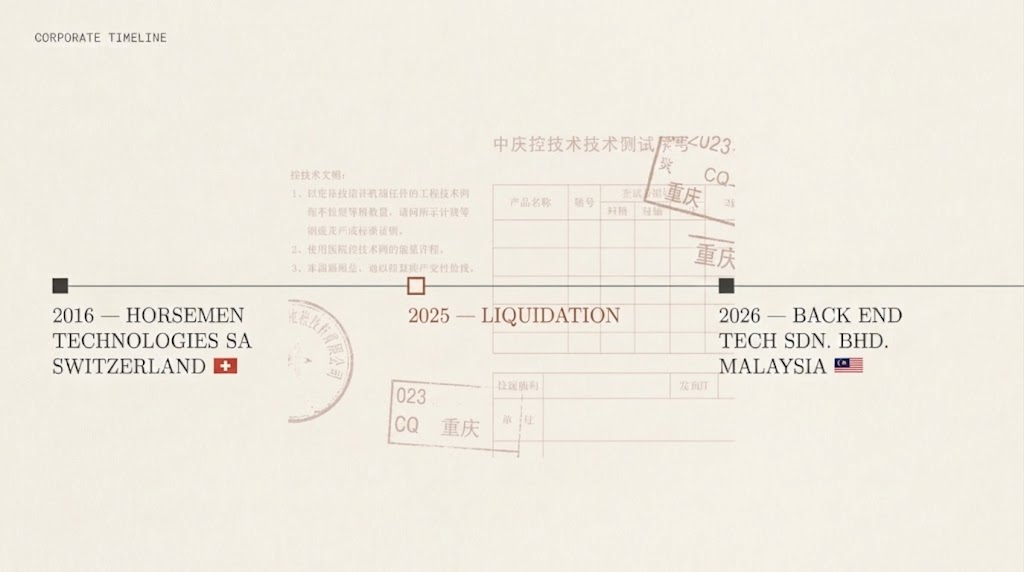
And that makes the original "Swiss messenger" label feel even more useless.
So by now we have a Swiss IP company, a very Chinese product footprint, a Chongqing-looking signing certificate, security docs that don’t agree with the App Store page, and then the whole thing suddenly reappears under a Malaysian company.
Not a honeypot evidence yet. But definitely enough weird shit to keep digging.
So who actually made the Potato?
That’s the annoying part because we still don’t have a clean answer.
Horsemen was the legal publisher, sure. But the technical trail keeps drifting east.
And once you follow the Chongqing clue properly, the story stops being about weird certificate fields.
You hit a Chinese cybersecurity company.
One whose surviving profile talks about network investigation, remote forensics, public-security clients, and for some fucking reason, lists Hacking Team and FinFisher among its competitors.