From Chongqing With Love
The Potato Files: Part II
Part I had a pretty weird little artifact:
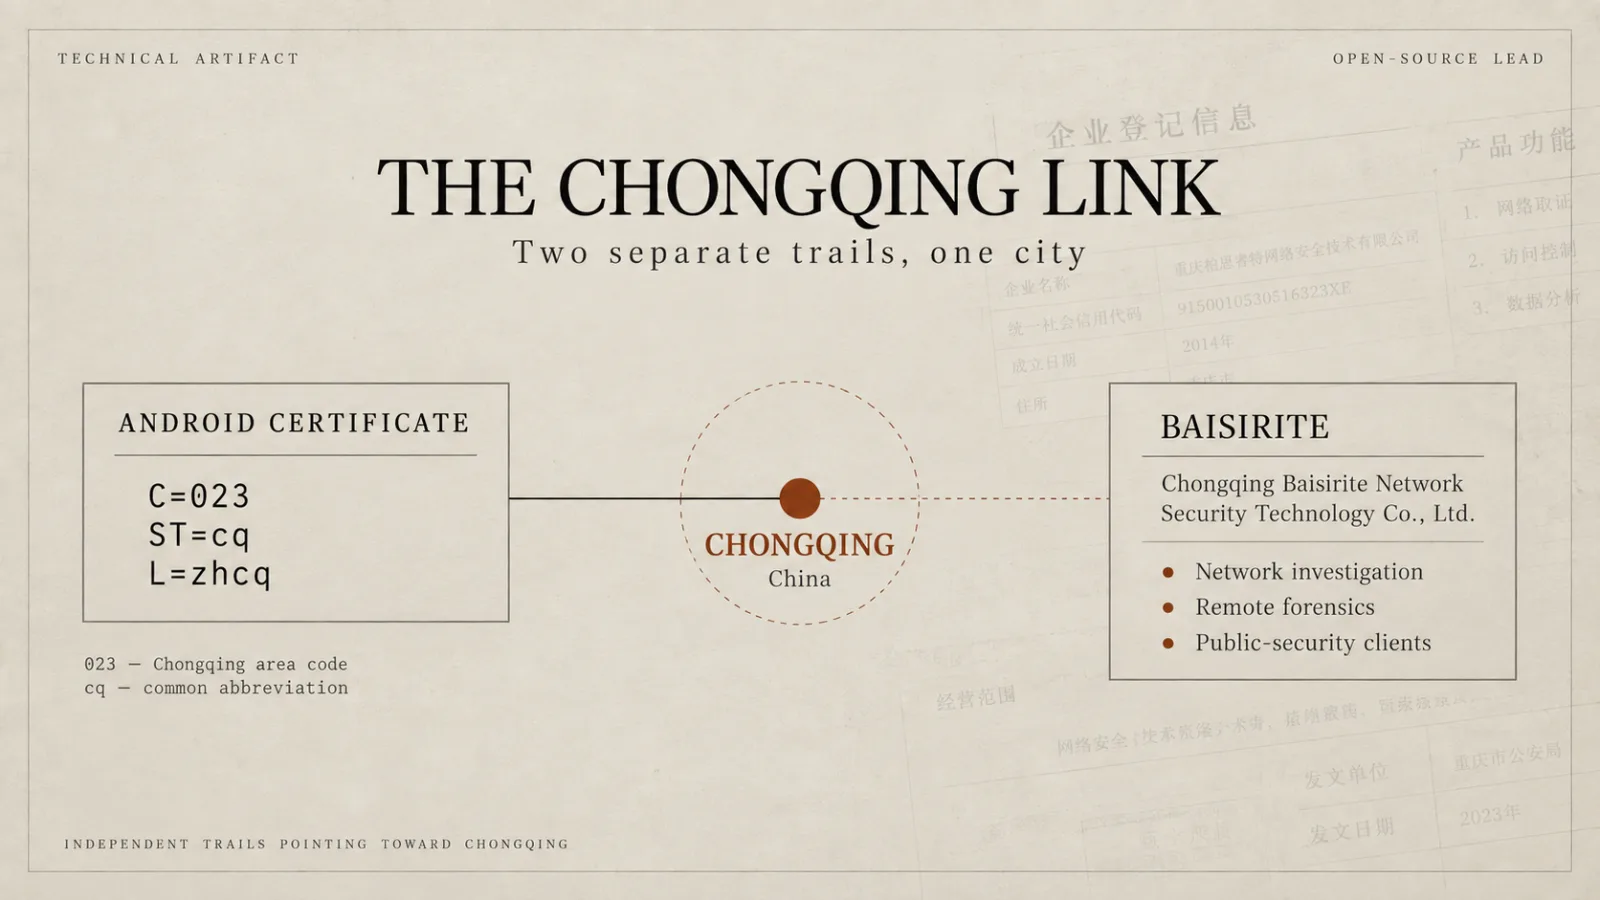
C=023
ST=cq
L=zhcq
A very Chongqing-looking Android certificate attached to a supposedly Swiss messenger. So naturally, my next question was:
Okay. What the fuck is in Chongqing?
And this is where the story gets a lot more interesting.
Meet Baisirite
There are old Chinese claims linking Potato’s development to a Chongqing company called:
重庆柏思睿特网络安全技术有限公司
or Chongqing Baisirite Network Security Technology Co., Ltd.
I’m not going to repeat the personal information that was dumped alongside those claims. That part is irrelevant anyway.
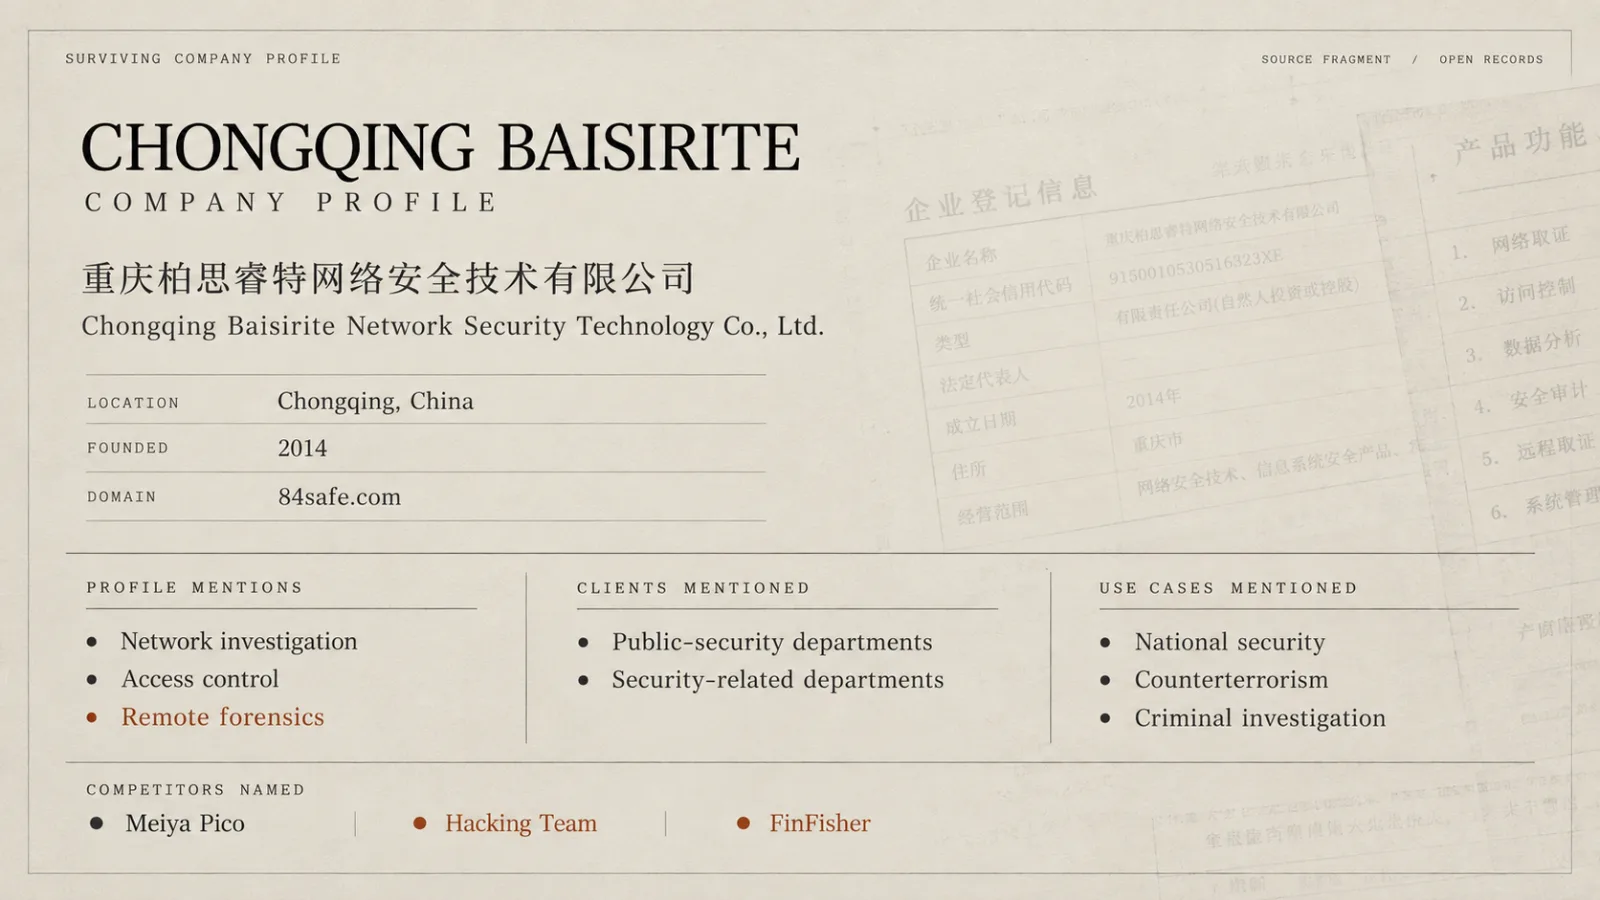
A surviving Chinese company profile lists it as an information-security company founded in Chongqing in 2014, with the old website 84safe.com
So far, boring and nothing special.
Then you get to the products.
The profile says Baisirite worked with:
服务于国家特殊部门的临侦设备
roughly: investigative / surveillance equipment for special state departments.
Then it gets more specific:
网络侦查系统、网络权限控制系统和远程取证
Network investigation systems.
Network access-control systems.
Remote forensics.
Well... That’s a little less boring, isn't it?
The same profile says its clients included:
公安、安全等相关部门
public-security and security-related departments
And that some products were used in:
国家安全、反恐、刑侦
national security, counterterrorism and criminal investigation.
And then there’s this beautiful little detail. The profile lists some of Baisirite’s competitors.
Domestic competitor: Meiya Pico.
Foreign competitors: Hacking Team, FinFisher.
Yeah, you read that correctly, exactly those Hacking Team and FinFisher.
That's not McAfee
If those names mean nothing to you, this is where context matters.
Hacking Team was an Italian company behind Remote Control System, spyware that Citizen Lab described as being marketed and sold exclusively to governments. Its capabilities included copying passwords, emails, files and instant messages, recording calls, and remotely activating microphones and webcams.
FinFisher was another commercial surveillance suite. Citizen Lab described it as sophisticated spyware sold exclusively to governments for intelligence and law-enforcement use.
So when Baisirite lists Hacking Team and FinFisher as competitors, we're clearly talking about the commercial surveillance / remote-intrusion market.
And if the Potato link is real, then we're no longer dealing with some random Chinese outsourcing shop.
Before we go full tinfoil
One caveat before we get carried away: all of that surveillance stuff comes from a surviving Chinese enterprise profile. I still haven't recovered Baisirite's original 84safe.com pages or a government procurement contract confirming who actually bought what.
So I'm not upgrading “public-security clients” into “Chinese intelligence contractor.”
Honestly, the profile is weird enough without us improving the story.
They weren't just selling PowerPoints either
There are a couple of independent traces showing Baisirite was an actual operating technology company.
A 2015 public corporate prospectus records a RMB 1 million contract from March 2014 involving Baisirite and an enterprise data-protection / data-loss-prevention system called I-Dun V3.1
So the cybersecurity side wasn’t invented by some random Telegram poster years later.
And, weirdly enough, Baisirite was also operating consumer mobile software.
China’s National Press and Publication Administration lists 重庆柏思睿特网络安全技术有限公司 as the operator of the mobile game 闲娱番茄麻将 in August 2017.
Which is useful for one simple reason:
it means the company wasn’t some pure enterprise-security consultancy that would have had no reason to touch Android/iOS consumer apps.
They were doing both.
Information security + consumer mobile software.
Right around the time Potato appeared.
That doesn’t magically connect the two, but it removes one pretty obvious objection:
Why the fuck would a surveillance/security company even be building a messenger?
Well... Apparently consumer mobile software wasn’t outside their wheelhouse.
Now go back to the certificate
Remember 023 / cq / zhcq?
The old claim points to a cybersecurity company in Chongqing.
Completely separately, Potato's original signing certificate points to... Chongqing.
And the company at the end of that allegation turns out to have a surviving profile full of remote forensics, network investigation and public-security/security-related customers.
Does that prove Baisirite built Potato?
Not yet.But I'm definitely not throwing that lead in the trash anymore.
I think the cleanest way to describe it is:
the allegation and the technical artifact independently point to the same city.
And once you get to that city, you find a company with a résumé that is extremely relevant to the exact threat model we’re investigating.
That’s enough to make the connection worth taking seriously.
And this is where it gets uncomfortable
Let’s assume for a second that the Baisirite link is real.
Not that Potato was a honeypot. Just that Baisirite actually built or helped build it.
Then the story becomes:
A company whose business included remote forensics and network investigation for security-related customers also worked on a private messaging platform.
A platform whose ordinary chats were historically cloud-based.
A platform whose modern successor now markets itself as universally end-to-end encrypted while its own privacy policy still describes separate Cloud Chats and Secret Chats.
That is one hell of a conflict of interest.
And suddenly the question from Part I sounds a little less stupid.
Not answered. Just less stupid.
Unfortunately, Chongqing isn't the end of it
At this point I thought the interesting part of the story was the Chinese company. It wasn't.
Because eventually you stop looking at Potato’s code and start looking at the people sitting inside Horsemen Technologies SA.
And one of those people takes this story from:
A weird Chinese cybersecurity rabbit hole
to:
Bruh... Switzerland, China, Malaysia — but why the fuck are we suddenly in Cambodia?